Provisioning is only the beginning
A successful deployment still needs an accountable owner, an approved purpose, a financial boundary and a defined end. Acumy keeps those conditions attached after resources reach the cloud.
One control plane for non-production infrastructure and AI-driven workflows, applying financial, operational and security guardrails across the entire workspace lifecycle.
“Deploy a Payments test environment for 12 hours, within a $100 budget.”
Cleanup covers the workspace’s supported resources and associated ancillary resources under the configured policy. Confirm provider and resource coverage in your demo.
A complete operating model
Capture purpose, ownership, workload, budget, policy and expiry before provisioning. Then keep that context attached through operation and retirement.
Why a dedicated control plane
It is created more frequently, changes more quickly and often exists for a limited purpose. Test environments, sandboxes, proofs of concept and model-validation workloads may be essential today and unnecessary tomorrow.
The tools used to provision infrastructure, enforce cloud security and analyse bills each solve part of the problem. Acumy connects the missing operational context across the entire lifecycle.
Understand the Acumy control modelA successful deployment still needs an accountable owner, an approved purpose, a financial boundary and a defined end. Acumy keeps those conditions attached after resources reach the cloud.
Tags are useful signals, but they are often inconsistent, incomplete or applied after creation. A Workspace holds the richer governance record that teams need to make decisions.
Traditional cost tools show what has already been consumed. Acumy introduces budget accountability at request time and retains the context needed to interpret spend later.
Developers, pipelines and AI agents can all create infrastructure. Acumy gives each route the same policy gate while preserving who or what initiated the request.
The platform in action · 86 seconds
See the workspace lifecycle: request, check, deploy, monitor and clean up. The current film also introduces commitment planning.
Explore the platformRequest to retirement
A governed path for developer requests, workflows and AI agents across AWS, Microsoft Azure and Google Cloud. Policy is not a one-time check. Budget, schedule, ownership and expiry continue to shape how the environment operates.
Govern before deployment
A Workspace is Acumy’s governed unit of non-production cloud. It combines the infrastructure request with its operational contract, so technical and financial context travels with the deployment instead of being reconstructed from tickets, tags and billing data later.
Actual product
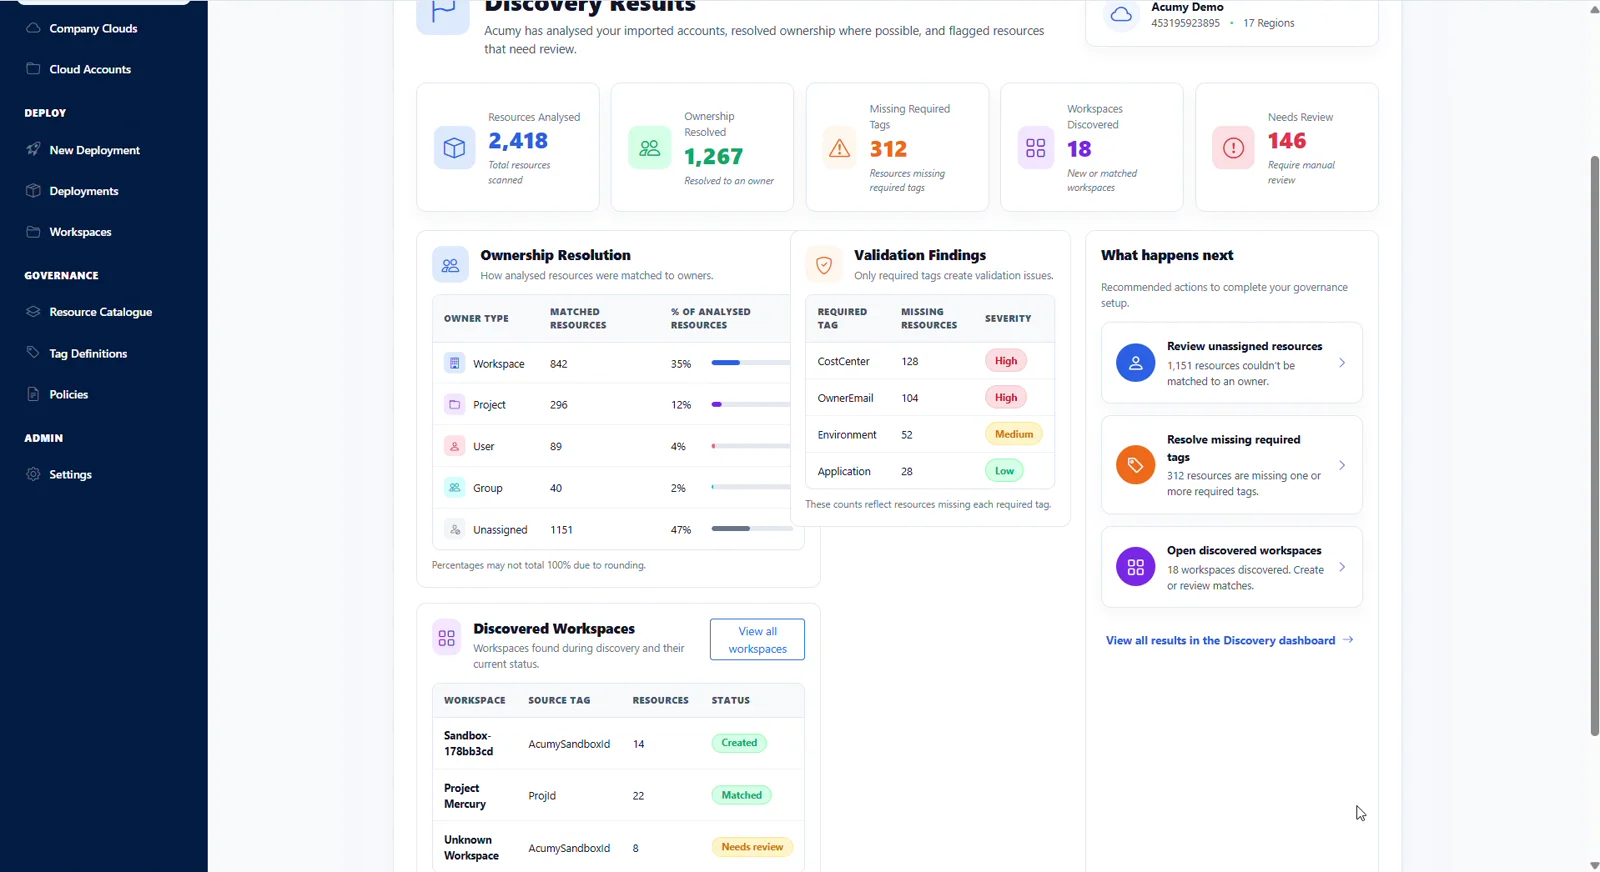
Acumy connects to cloud accounts, stages what it finds and surfaces ownership, tagging and Workspace context. Teams can review gaps in the current estate before applying the governance model to new requests.
One connected platform
Start with the estate you have. Give teams a governed route to new environments. Keep ownership, policy and lifecycle connected until the work is done.
Surface resources, owners, tag gaps and missing operational context across cloud accounts.
Explore Discovery 02Turn each request into a policy-checked Workspace with an owner, purpose, budget and end date.
Explore governance 03At expiry, run configured cleanup across associated resources, including supported ancillary resources, and review the result.
Explore the lifecycleAI infrastructure governance
AI agents can create infrastructure at machine speed and through workflows that may never involve a conventional service ticket. Acumy gives agent-created environments their own identity, permissions, accountable team, budget and time boundary while preserving governed self-service.
One context, multiple teams
Each team keeps its own responsibilities while working from the same operating context. Engineering requests approved capacity, CloudOps sets operational restrictions, Security defines access controls and FinOps sets budgets and attribution.
Request approved, reusable environments while ownership, limits and lifecycle stay visible.
Apply policy and access before provisioning, then automate renewal, expiry and retirement.
Connect budgets and cost responsibility to the reason every environment exists, then review usage with ownership and lifecycle still attached.
Set identity, access and security boundaries for people and authorised agents, with decisions recorded across the workspace lifecycle.
Trust & security
Acumy separates discovery from authorised control actions, works through scoped cloud identities and preserves a record of the decisions made throughout each Workspace lifecycle.
Las Vegas · Nov. 30 – Dec. 4, 2026
The Acumy team will be in Las Vegas meeting cloud, platform and FinOps leaders and running private product demonstrations at The LINQ.
Book a private demoAcumy is attending independently and is not an AWS exhibitor or sponsor.
Control non-production by design